
Go>Sign Desktop Requests
Create a Go > Sign Desktop Certificate Request
Create a Go > Sign Desktop Certificate Using a Vetting Form with SDN/SAN Mappings
Submit a Certificate Request based on Go>Sign Desktop Profile
Expand Requests > Certificate Requests from the left menu pane. The Certificate Requests listing screen will appear.
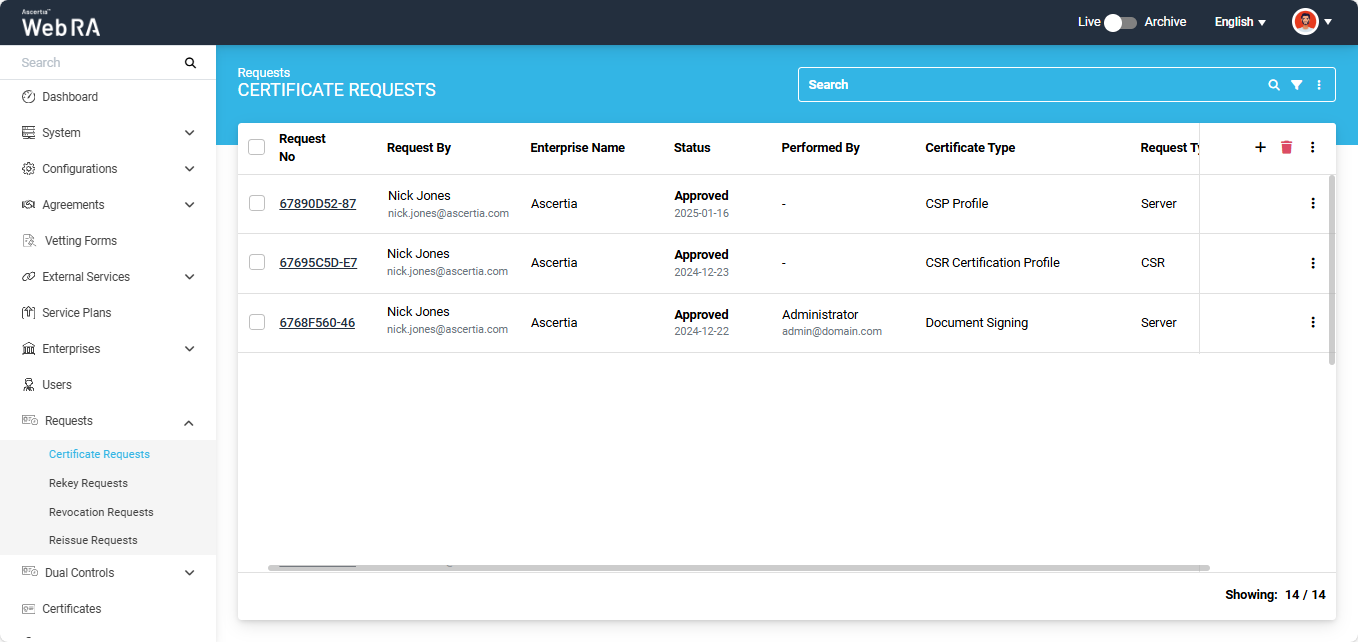
Click the + button in the grid header to access the Create Request screen. Select the Enterprise name from the dropdown, choose the Certificate Type, and click 'Create'.
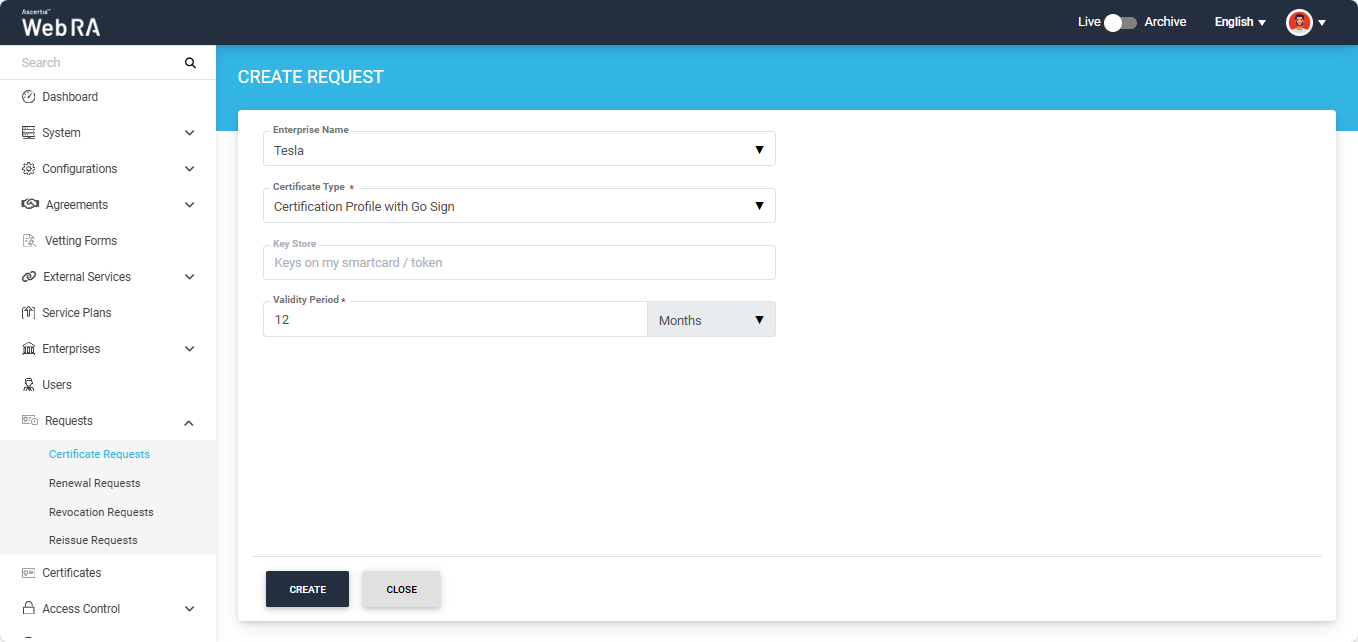
Note: A checkbox titled ‘Generate a certificate on behalf of the user’ will appear on this screen if the policy for this option is enabled in the Enterprise > Policies section.
Enabling this checkbox will allow the operator to generate a certificate on behalf of the user.
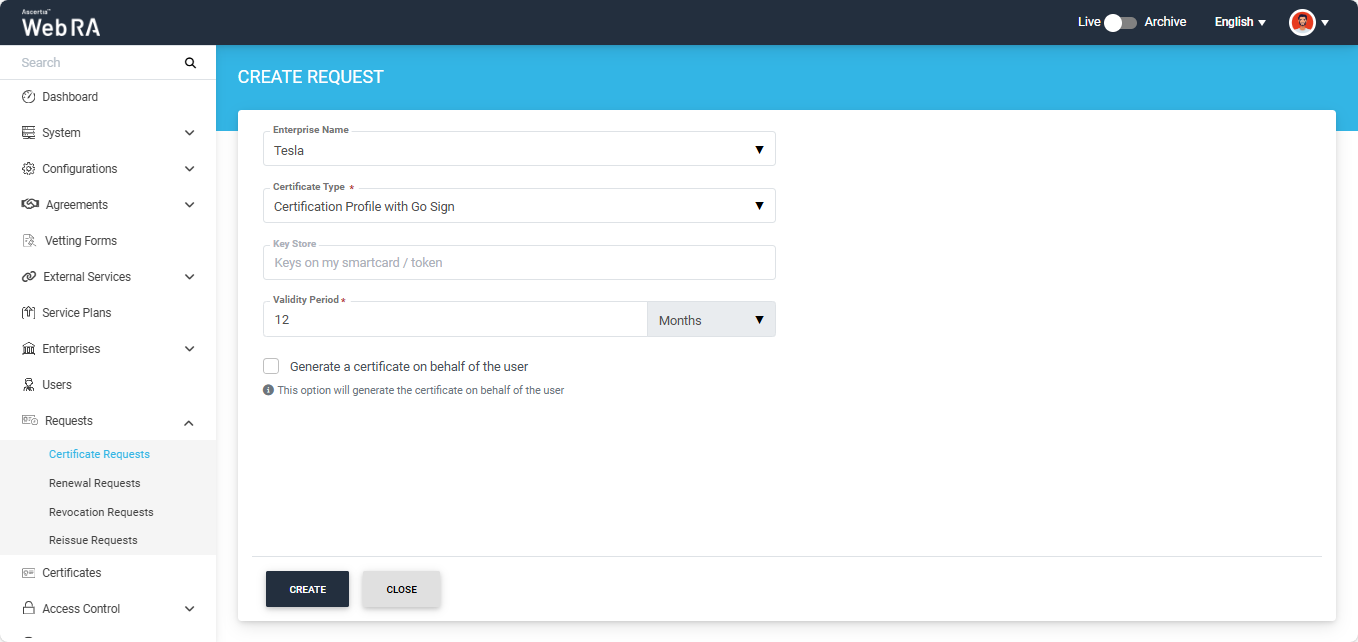
A Welcome Note screen will appear. Enable the ‘I allow the use of my data for processing certificate application by Enterprise Name’ and click next.
|
|
The 'Welcome Note' screen will only appear if the operator has enabled customised 'Request Notes' in the ‘Notification’ section of the Enterprise to which the user belongs to. |

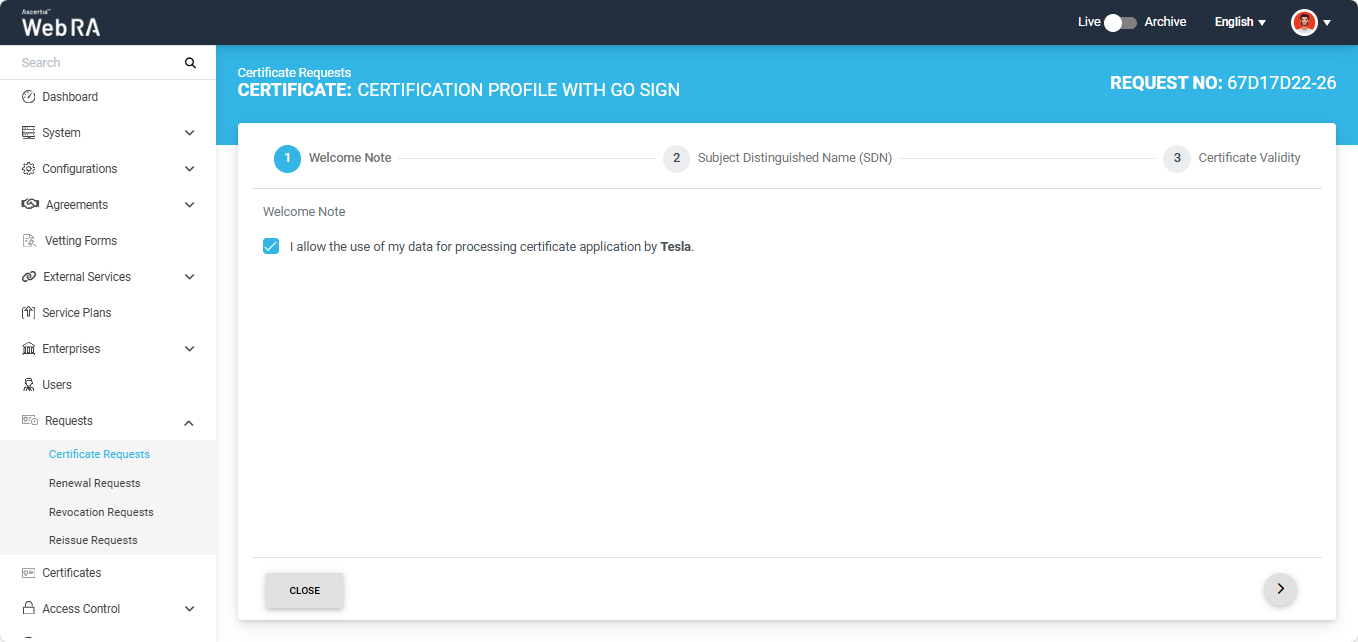
Once you agree to the Welcome Note and click Next, the ‘Subject Distinguished Name (SDN) screen will appear. Enter the required details in the respective fields and click 'Next'.
Country, State, Locality and Postal Code in a Certificate Request
When you create a certificate request, you may need to enter the certificate holder's Country, State, Locality (city) and Postal Code. Depending on how the certificate type is set up, these fields appear on the Subject Distinguished Name (SDN) screen.
|
Field |
Description |
|
Country |
Select the country. Only the countries allowed by your administrator are displayed. The country field will be pre-selected according to the country selected under the Enterprise > Profile > Organisation Information. |
|
State |
Select the state or province from the list. Only the states or provinces associated with the selected country are displayed. |
|
Locality |
Select the city from the list. This field is available only after a state or province has been selected. You can type in the field to search for a city. |
|
Postal Code |
Enter the postal code in the format required by the selected country. If the entered postal code does not match the required format, an error message is displayed. For example: "The postal code does not match the format of the selected country. It must be 5 characters." |
Note:
- On this screen the field names always stay the same. For example, State is still called State even if the country uses provinces.
- If you change the country, the State and Locality are cleared and you need to select them again.
- Ensure that the CSR uploaded with the certificate request contains the correct country, state or province, and locality details.
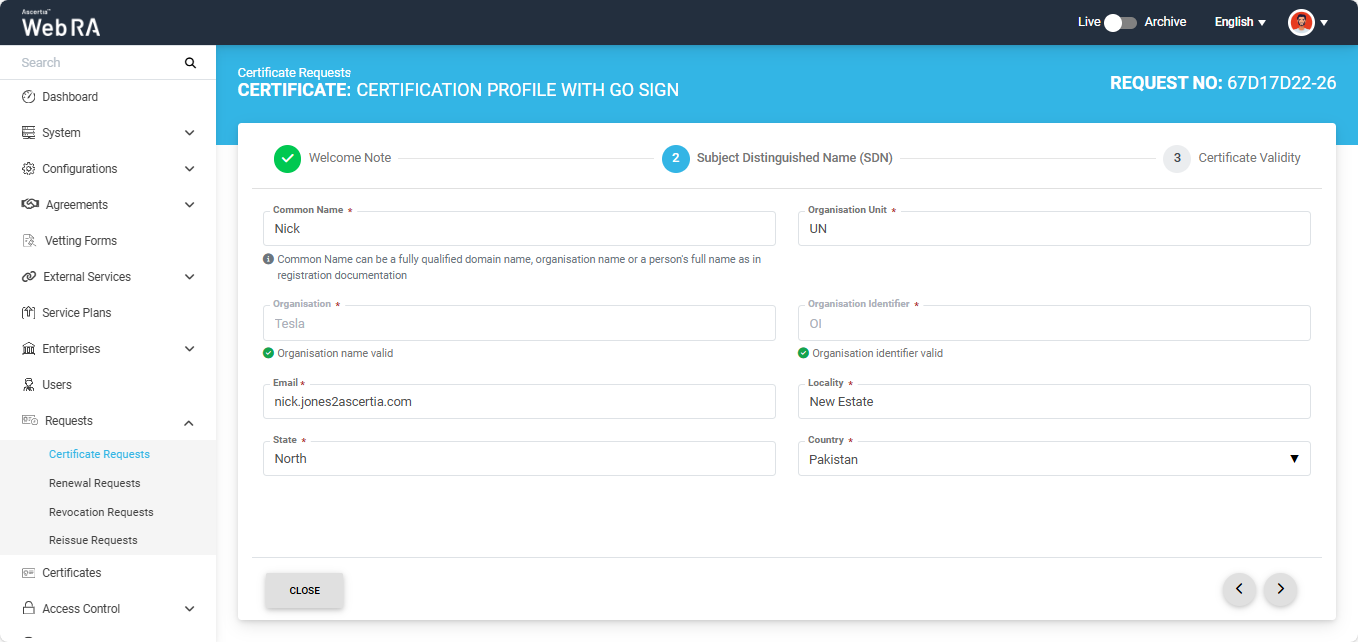
The Certificate Validity screen will appear. Enter the validity period and click 'Generate'.
The systen will display a 'Go Sign Token' dialog with a dropdown named 'Token'. You will be required to select the token for the certificate being generated. After selecting the token, click 'Ok'.
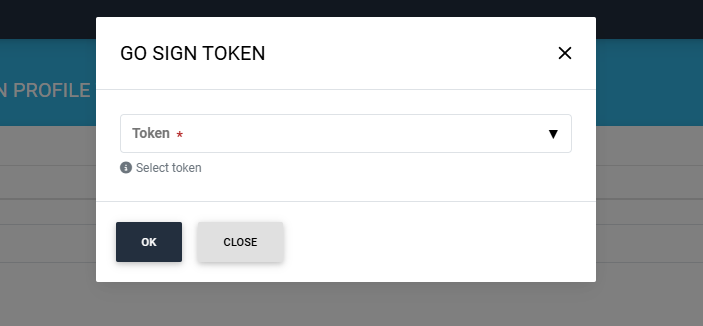
The system will generate the CSR and issue the certificate. The 'Certificate Generated' message will appear at the right bottom of the screen.
Note: If the ‘Generate a certificate on behalf of the user’ checkbox is enabled, the system will display an additional screen titled ‘User Information’ next to the 'Certificate Validity' screen.
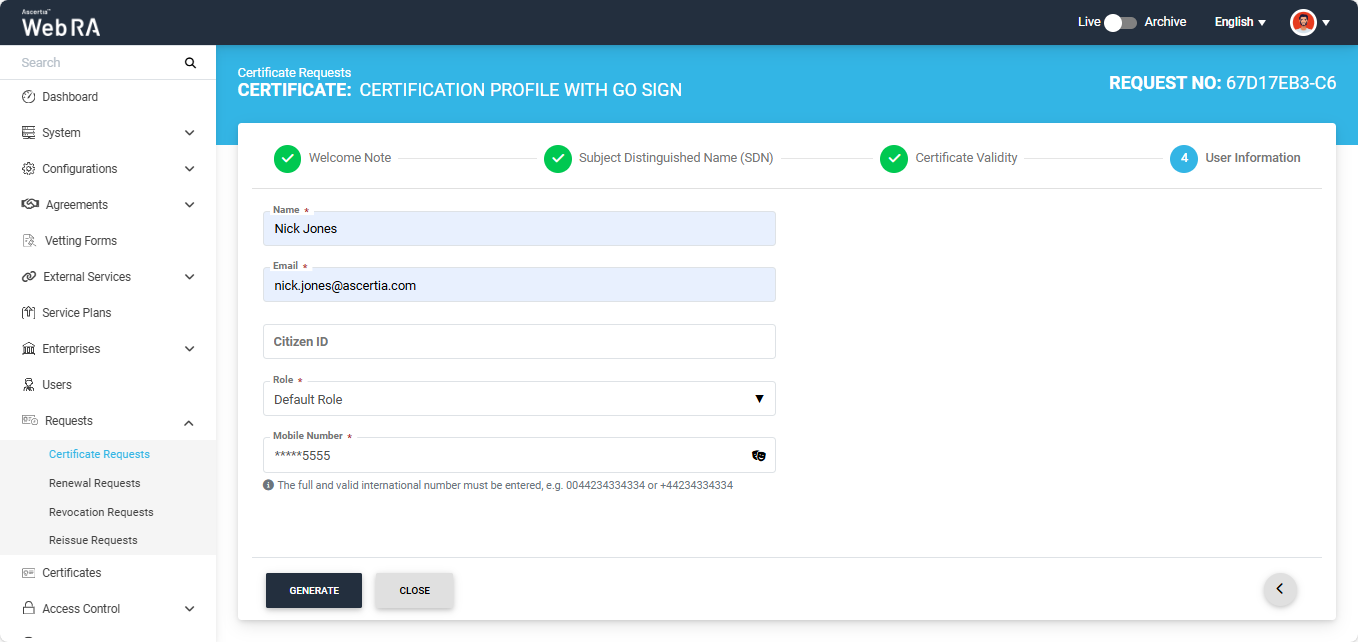
On this screen, you will be required to enter and select the Name, Email, Citizen ID, Mobile Number, and Role of the user for whom the certificate is being generated.
After entering the details, click ‘Generate’.
Note: If the operator is creating a certificate request on behalf of a user using a Smart Card/Token profile, and 'None' is selected in the 'Mechanism' dropdown of the certification profile, the certificate will not be generated. Therefore, when creating a certificate on behalf of a user, you must select any other option (i.e., Email, SMS, or Both) from the dropdown. To read more about the 'Mechanism' dropdown, navigate to the Certification Profiles section.
The systen will display a 'Go Sign Token' dialog with a dropdown named 'Token'. You will be required to select the token for the certificate being generated. After selecting the token, click 'Ok'.
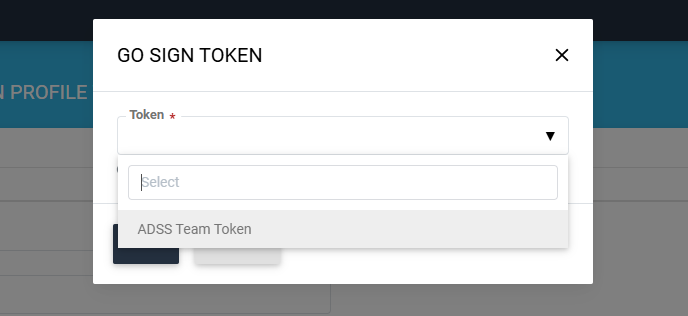
The system will create an account for the user and generate the certificate.
The system will auto-generate the PIN or PUK value based on the configured policies in the Enterprises > Policies section. If there is no policy enabled, the system will auto-generate a random value for PIN or PUK. The generated values will be shared with the user via Email or SMS (depending upon the mechanism selected during the creation of certification profile). The user will also receive an email regarding the account and certificate creation and is prompted to activate their account.
Note: If the certificate is being created for a user who does not exist in the system, a new account will be created for the user along with the certificate. If the user already has a registered account in the WebRA system, only the certificate will be created. The user will be notified via email about the certificate generation. Meanwhile, if the user exists in the system but is not part of the enterprise where the certificate is being created, the system will send an invitation for the user to join that enterprise and will generate the certificate as well.
If 'Dual Control' for request section or 'Special Permissions' setting is enabled in the certification profile of Smartcard/Token in ADSS Web RA, the 'Go Sign Token' dialog will also display a 'None' option in the dropdown.
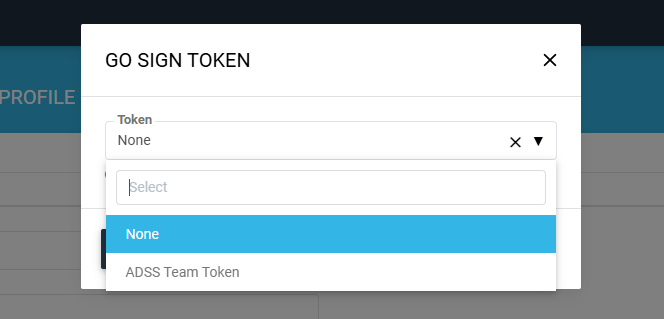
If you select the 'None' option from the dropdown and submit the request, the certificate request will be submitted without creating CSR. However, if you select a token from the dropdown, the system will first create a CSR and then submit the certificate request.
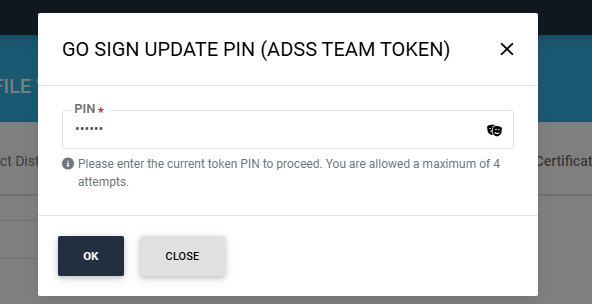
Note: If the token password previously generated by the ADSS Web RA system has been changed through the 'SafeNet Authentication Client', the system will display the 'Go Sign Update PIN' dialog when you attempt to generate a new certificate request from the same token.
You will be required to enter the updated token PIN to proceed.
Note: If the setting for Digital Onboarding is enabled in the Certification Profile, clicking the 'Generate' button displays a dialog containing the providers configured in the selected Digital Onboarding connector.
Select the required provider from the given options.
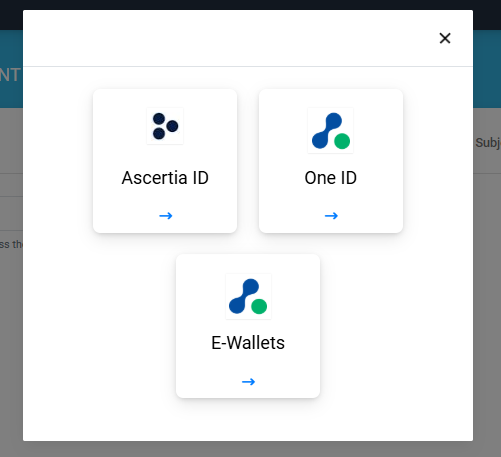
The system then displays a QR code. Scan the QR code using the Digital Onboarding mobile application.
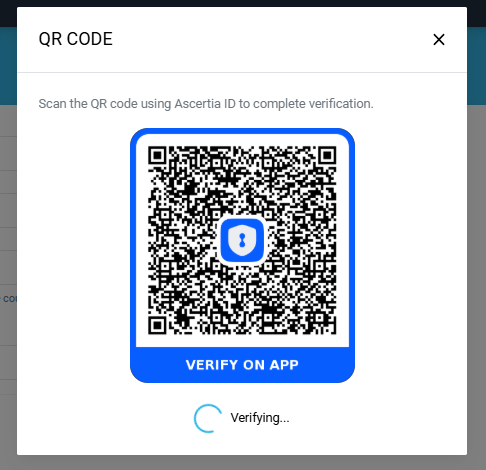
After scanning the QR code, complete the identity verification process by providing the required documents as configured in the Digital Onboarding policy.
Once the identity verification process is completed successfully, the QR code will disappear and the certificate request will be generated.
Create a Go > Sign Desktop Certificate Using a Vetting Form with SDN/SAN Mappings
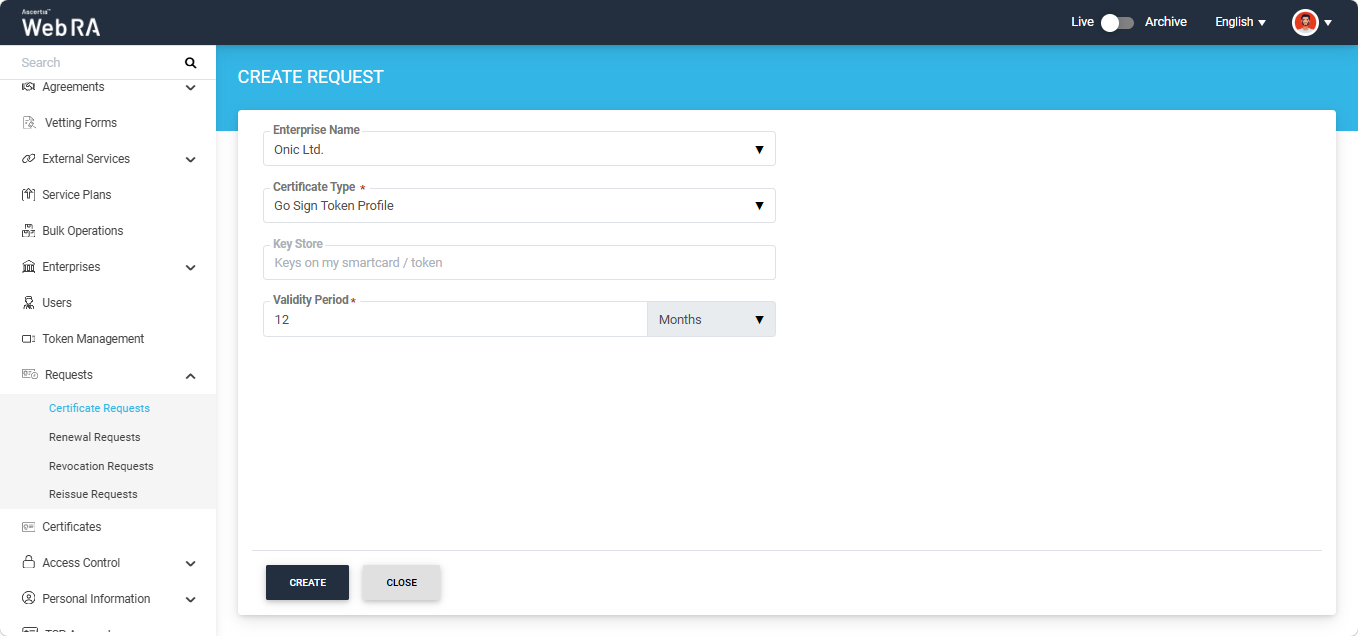
Expand Requests > Certificate Requests from the left menu pane. The Certificate Requests listing screen will appear.
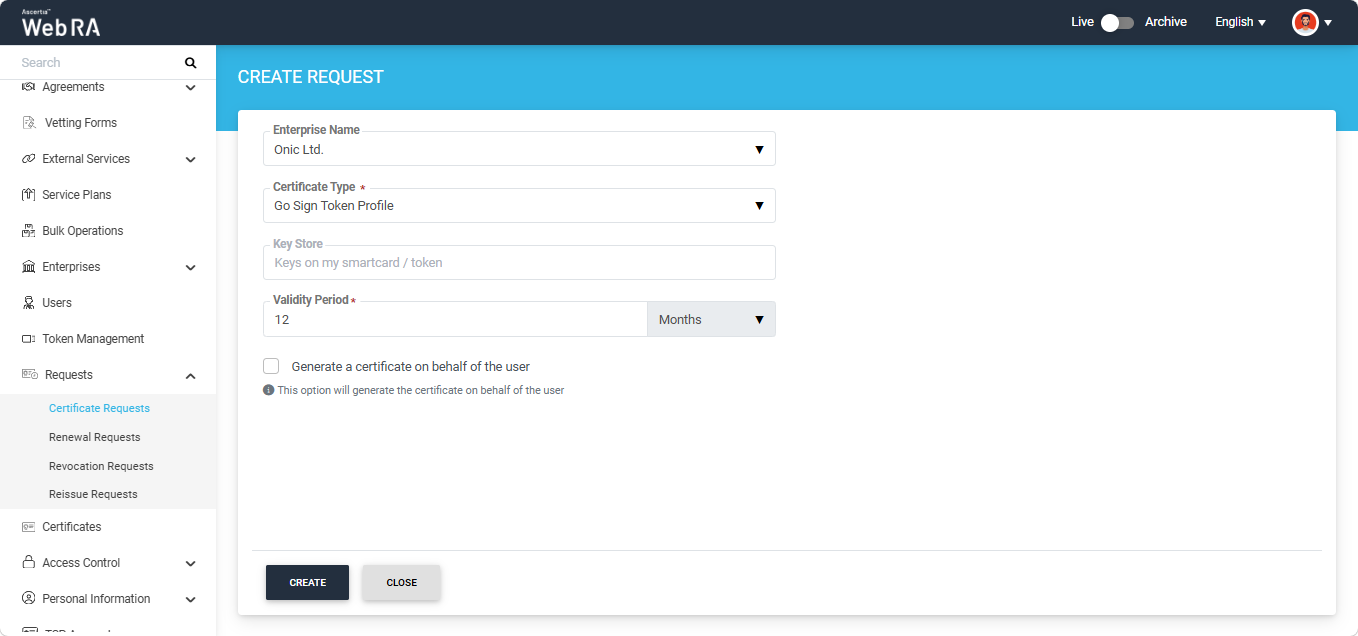
Click the + button in the grid header to access the Create Request screen. Select the Enterprise name from the dropdown, choose the Certificate Type, and click 'Create'.
|
|
Note: A checkbox titled ‘Generate a certificate on behalf of the user’ will appear on this screen if the policy for this option is enabled in the Enterprise > Policies section. Enabling this checkbox will allow the operator to generate a certificate on behalf of the user. |
The system displays the certificate request, where you can enter the required information in different sections according to your requirements.
If any fields in the vetting form are mapped to Subject Distinguished Name (SDN) or Subject Alternative Name (SAN) fields, the vetting form appears as the first step in the certificate request. The user must enter the details in the vetting form before proceeding to the remaining sections of the certificate request. The values entered in the vetting form are used to populate the corresponding mapped SDN/SAN fields.
|
|
Note:
|
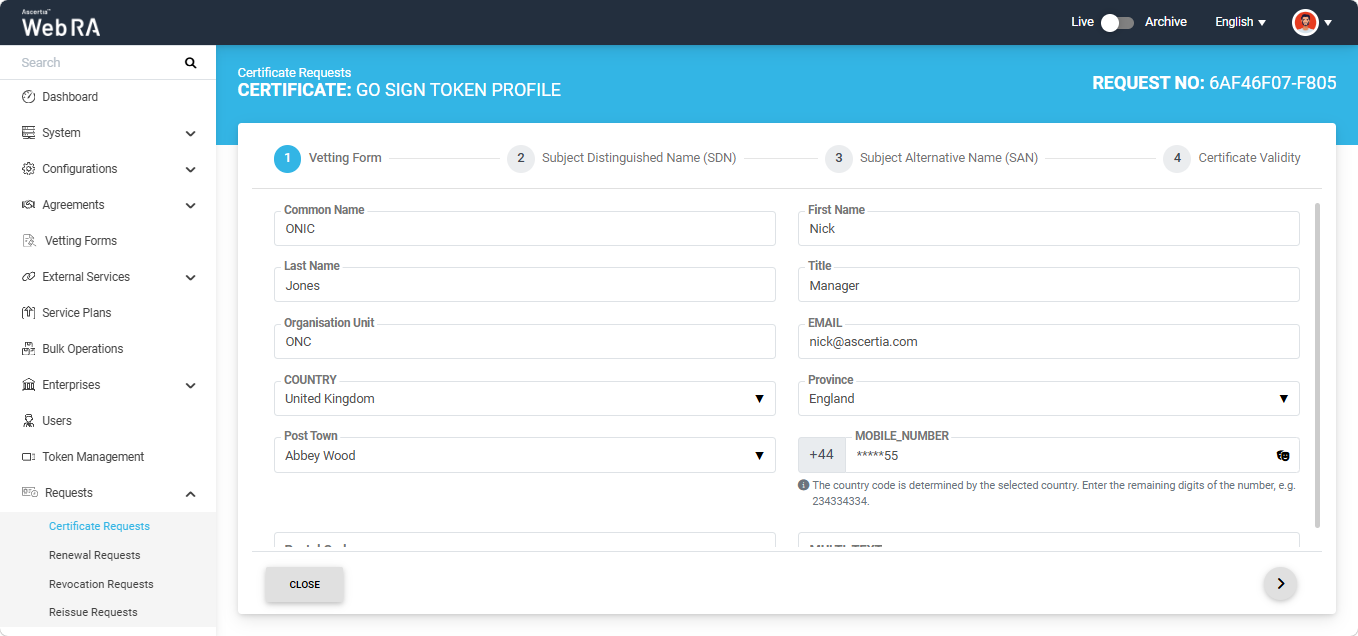
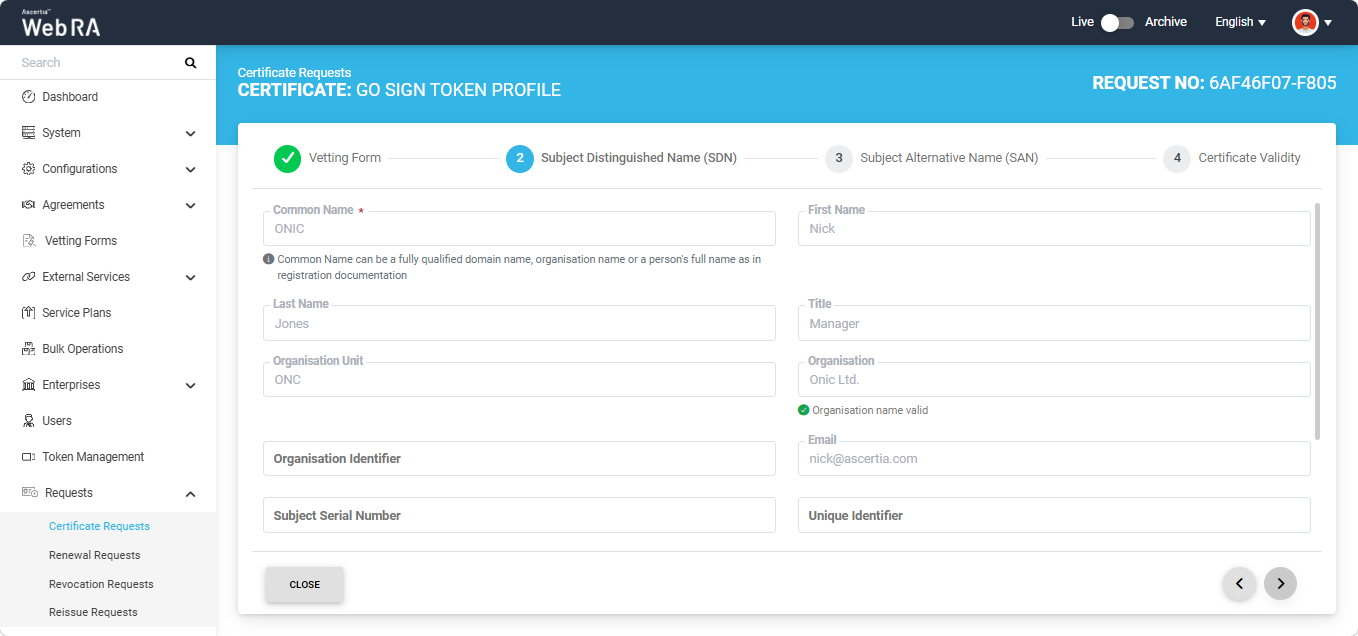
After entering the information in the Vetting Form fields, click the next ‘>’ button to proceed to the Subject Distinguished Name (SDN) screen.
|
|
Note:
|
If an SDN field is not mapped to a Vetting Form field and is not configured as fixed in the ADSS Certification Profile, the field remains enabled, allowing you to enter a value according to your requirements.
After reviewing and entering the required values, click the next ‘>’ button to navigate to the Subject Alternative Name (SAN) screen.
|
|
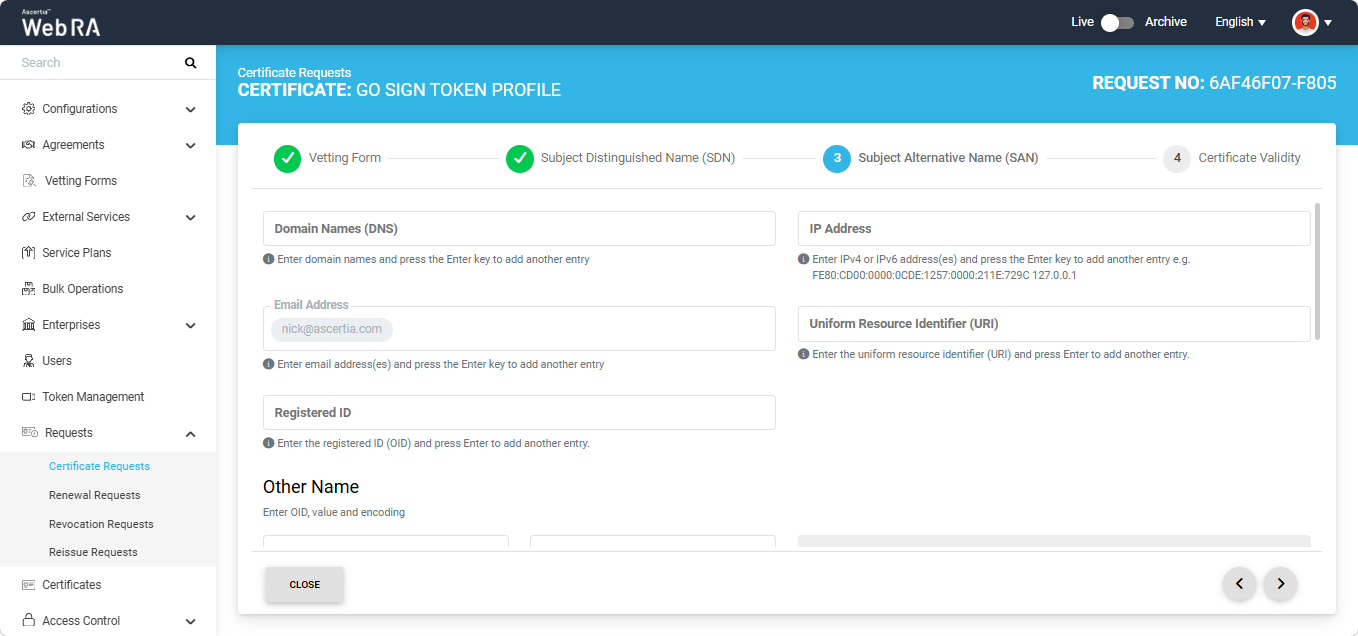
Note: ADSS Web RA now supports the following additional Subject Alternative Name (SAN) fields:
When these SAN fields are configured in the ADSS Certification Profile, the corresponding fields are also supported in ADSS Web RA. Furthermore, ADSS Web RA now supports additional encoding methods for the Directory Name and EDI Party Name SAN fields. The newly supported encoding methods are:
|
|
|
Note:
|
If a SAN field is not mapped to a Vetting Form field and is not configured as fixed in the ADSS Certification Profile, the field remains enabled, allowing you to enter a value according to your requirements.
After reviewing and entering the required values, click the next ‘>’ button to navigate to the ‘Certificate Validity’ screen.
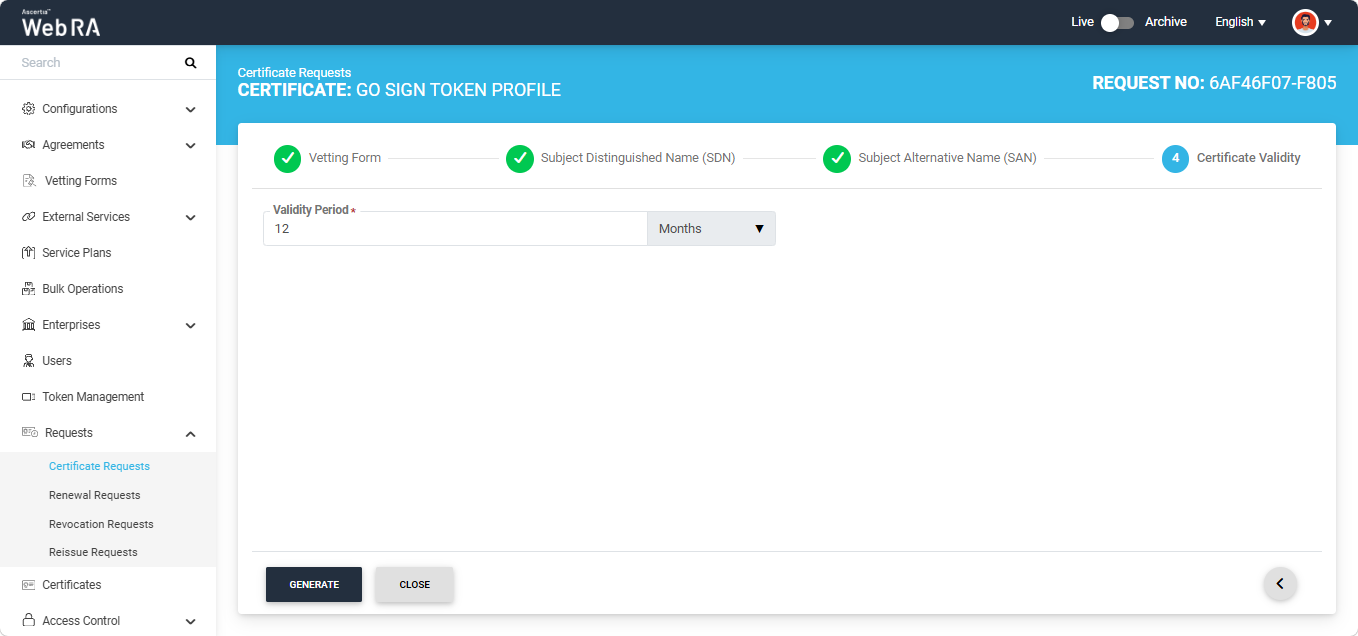
The Certificate Validity screen will appear. Enter the validity period and click 'Generate'.
The systen will display a 'Go Sign Token' dialog with a dropdown named 'Token'. You will be required to select the token for the certificate being generated. After selecting the token, click 'Ok'.
The system will generate the CSR and issue the certificate. The 'Certificate Generated' message will appear at the right bottom of the screen.
Note: If the ‘Generate a certificate on behalf of the user’ checkbox is enabled, the system will display an additional screen titled ‘User Information’ next to the 'Certificate Validity' screen.
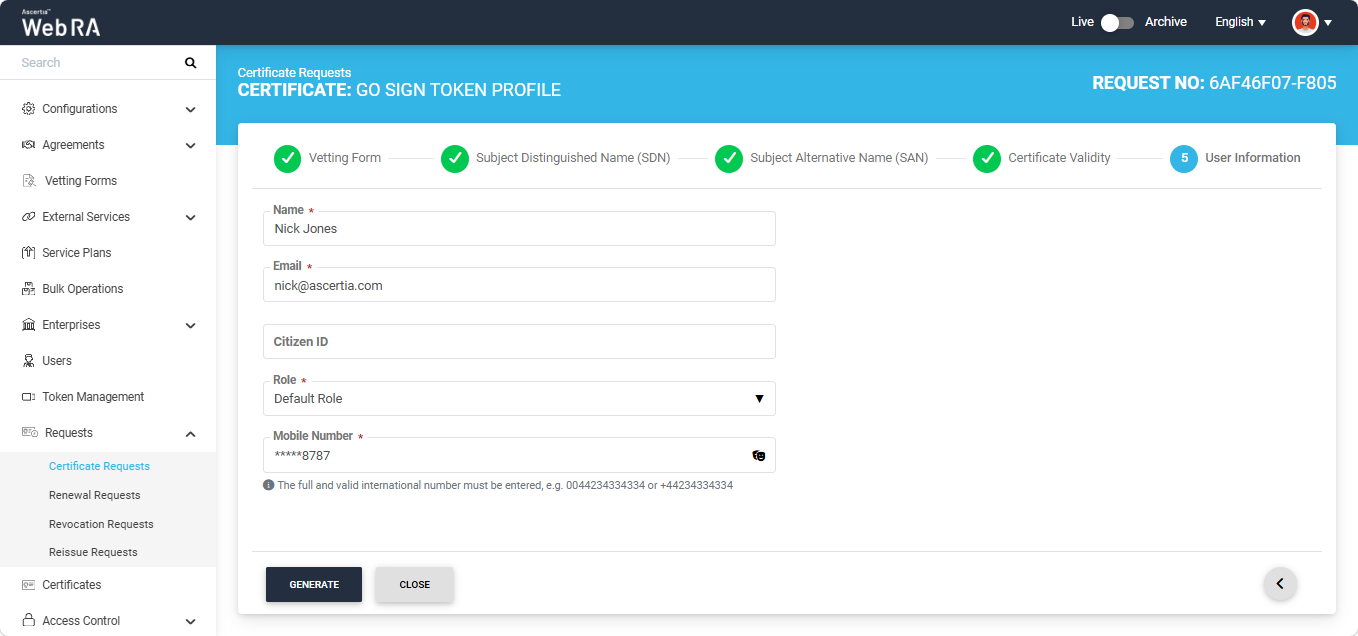
On this screen, you will be required to enter and select the Name, Email, Citizen ID, Mobile Number, and Role of the user for whom the certificate is being generated.
After entering the details, click ‘Generate’.
Note: If the operator is creating a certificate request on behalf of a user using a Smart Card/Token profile, and 'None' is selected in the 'Mechanism' dropdown of the certification profile, the certificate will not be generated. Therefore, when creating a certificate on behalf of a user, you must select any other option (i.e., Email, SMS, or Both) from the dropdown. To read more about the 'Mechanism' dropdown, navigate to the Certification Profiles section.
The systen will display a 'Go Sign Token' dialog with a dropdown named 'Token'. You will be required to select the token for the certificate being generated. After selecting the token, click 'Ok'.
The system will create an account for the user and generate the certificate.
The system will auto-generate the PIN or PUK value based on the configured policies in the Enterprises > Policies section. If there is no policy enabled, the system will auto-generate a random value for PIN or PUK. The generated values will be shared with the user via Email or SMS (depending upon the mechanism selected during the creation of certification profile). The user will also receive an email regarding the account and certificate creation and is prompted to activate their account.
Note: If the certificate is being created for a user who does not exist in the system, a new account will be created for the user along with the certificate. If the user already has a registered account in the WebRA system, only the certificate will be created. The user will be notified via email about the certificate generation. Meanwhile, if the user exists in the system but is not part of the enterprise where the certificate is being created, the system will send an invitation for the user to join that enterprise and will generate the certificate as well.
If 'Dual Control' for request section or 'Special Permissions' setting is enabled in the certification profile of Smartcard/Token in ADSS Web RA, the 'Go Sign Token' dialog will also display a 'None' option in the dropdown.
If you select the 'None' option from the dropdown and submit the request, the certificate request will be submitted without creating CSR. However, if you select a token from the dropdown, the system will first create a CSR and then submit the certificate request.
Note: If the token password previously generated by the ADSS Web RA system has been changed through the 'SafeNet Authentication Client', the system will display the 'Go Sign Update PIN' dialog when you attempt to generate a new certificate request from the same token.
You will be required to enter the updated token PIN to proceed.