
RAS Certification Profile
RAS Certification Profile
Expand External Services > Certification Profiles from the left menu. The system will display the certification profiles listing screen.
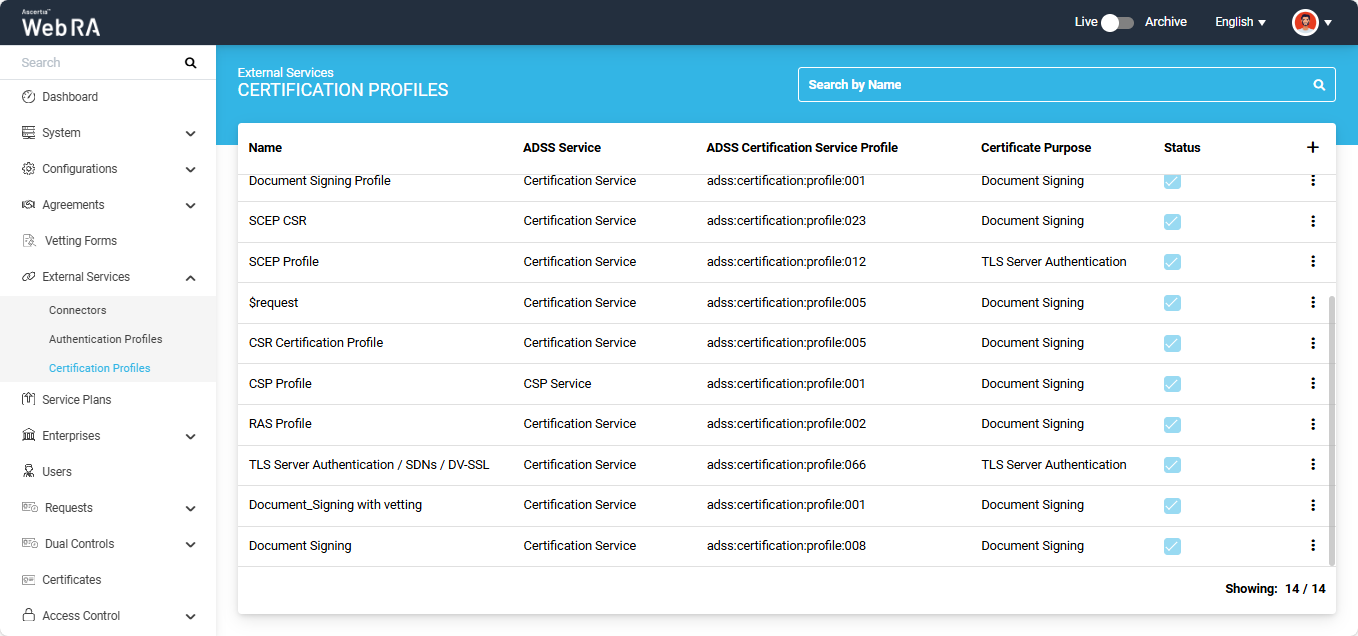
To add a new certification profile, click the ‘+’ button on the left side of the table header. The system displays the ‘Profile’ screen.
The Profile screen consists of the following two sections:
- Basic Information
- Service
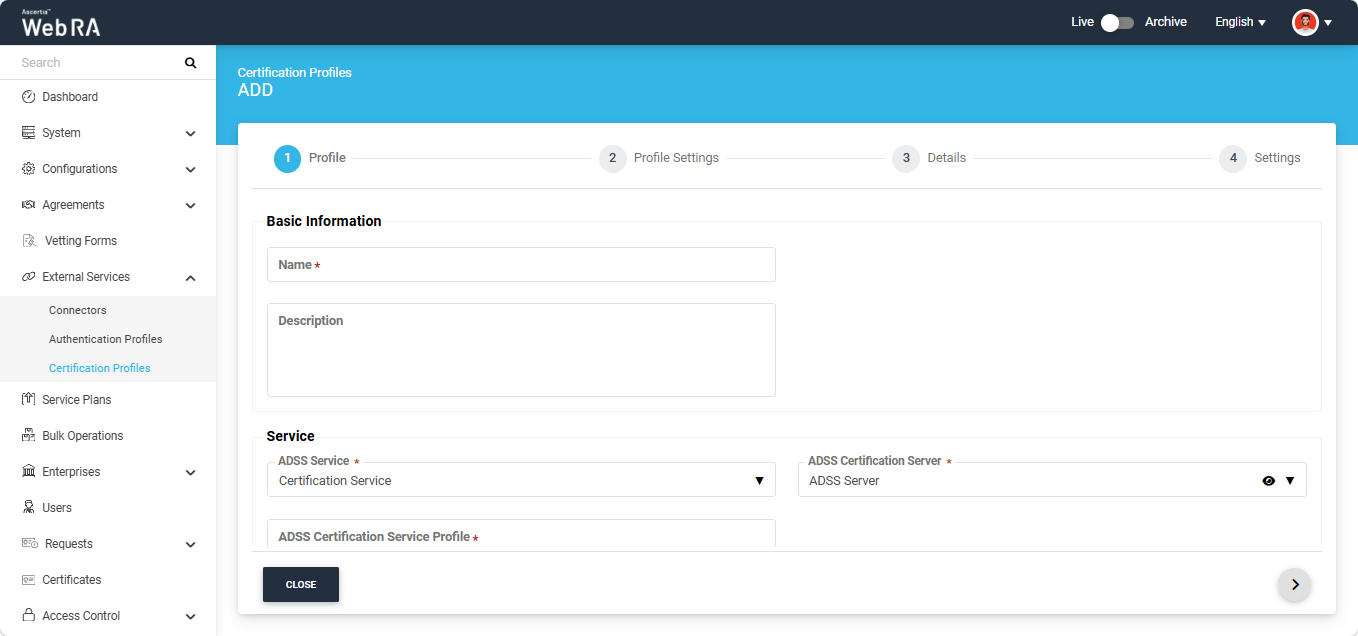
Basic Information
The Basic Information section displays the following fields:
|
Field |
Description |
|
Name |
Specify a unique name for this profile. |
|
Description |
Specify any description related to this certification profile. (Optional) |
Service
The Service section displays the following fields:
|
Field |
Description |
|
ADSS Service |
This field will display the ADSS Services (i.e. Certification Service and CSP Service) that are available for ADSS Web RA. Select the ‘Certification Service’ option from the dropdown. |
|
ADSS Certification Server |
This field will display the list of active ADSS connectors in ADSS Web RA. Select the one to use for this certification service profile, for example: 192.168.2.64. |
|
ADSS Certification Service Profile |
In this field, enter the certification profile that you created on the ADSS Sever, for example: adss:certification:profile:001. |
|
Active |
Select this checkbox to make the profile active. Inactive profiles cannot be associated with a Service Plan. |
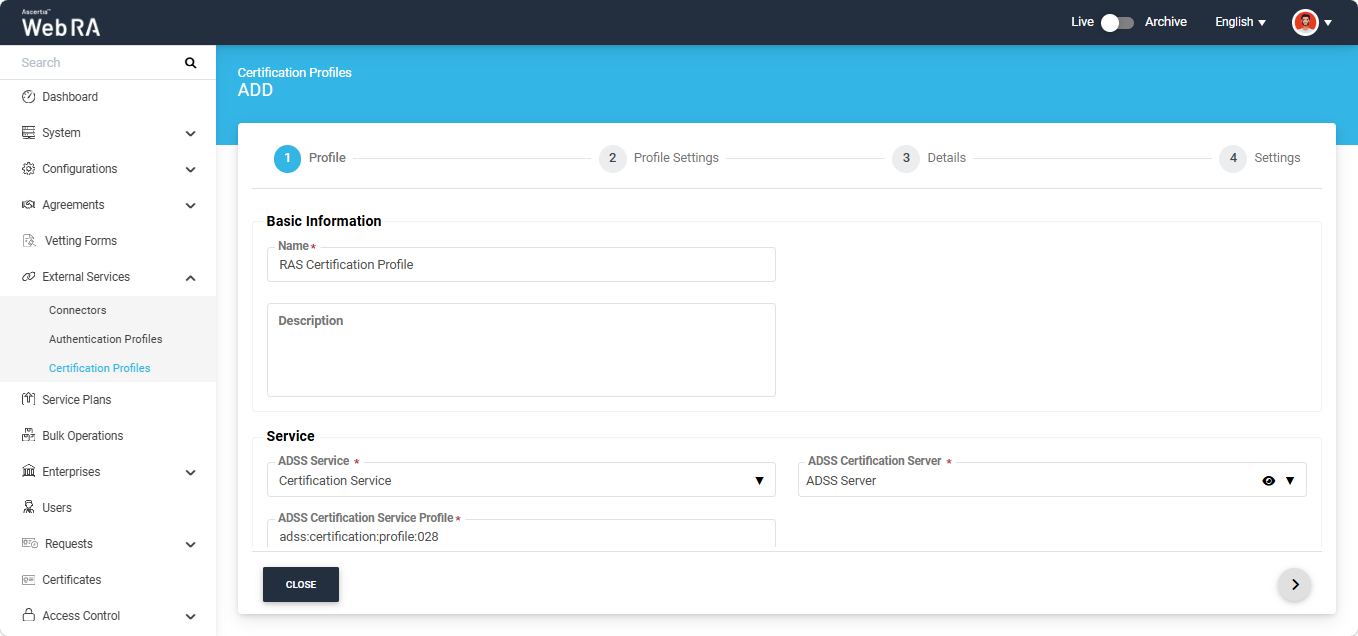
You can view the details of the selected ADSS connector by clicking the ‘Eye’ icon next to the connector name. When you click the icon, the system displays the ‘Connector’ dialog on the screen containing the information.
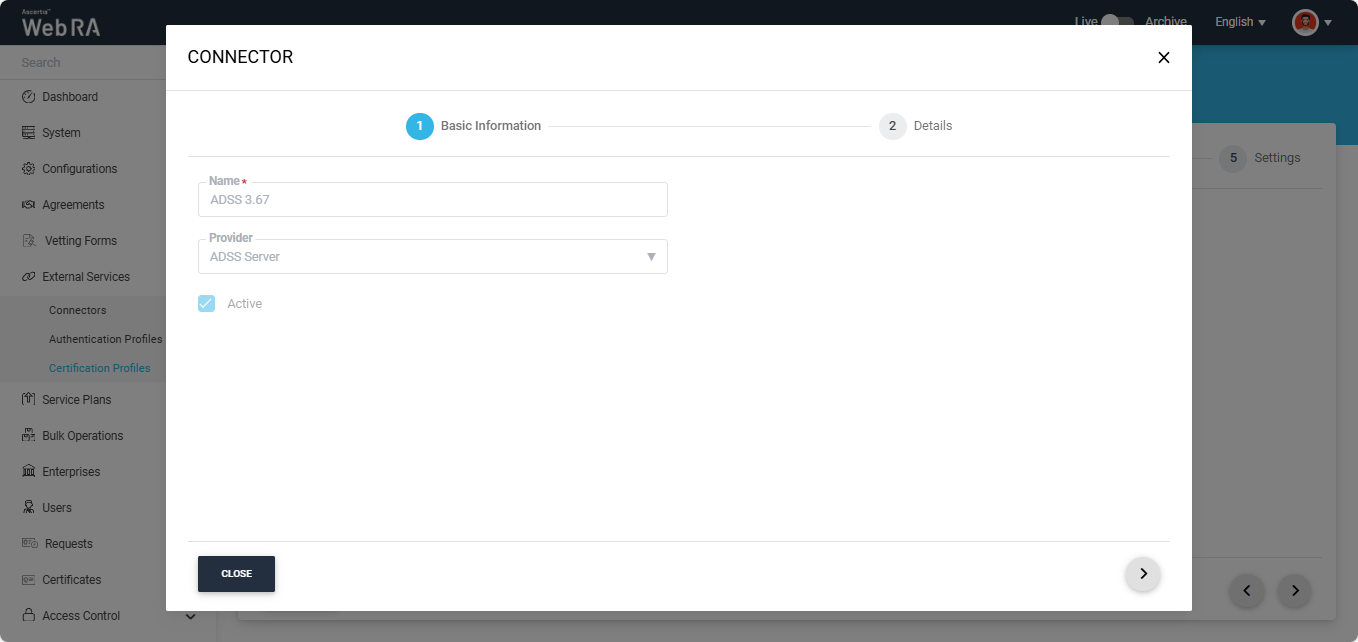
To view complete details of the connector, navigate to the ‘Details’ tab.
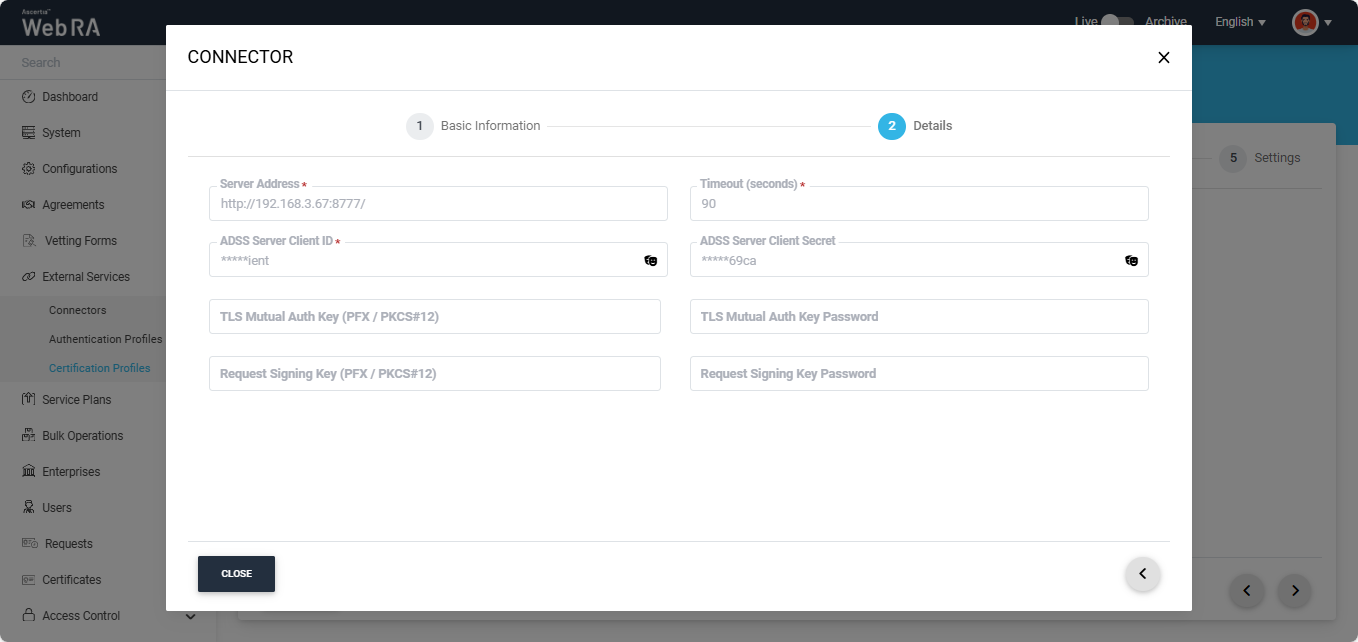
After providing the required information on the 'Profile' screen, click the next ‘>’ button to proceed to the ‘Profile Settings’ screen.
Profile Settings
The Profile Settings screen consists of the following sections:
- Certificate Information
- Registration Authority Server
- Certificate Information
The Certificate Information section displays the following fields:
|
Field |
Description |
|
Issuer Name |
It will display the issuer CA name. (This field will appear in disabled form) |
|
Certificate Purpose |
This field displays the certificate purposes, which comes from ADSS Server based on the selected certification profile. A certificate is generated based on the provided certification profile ID, and it will be in a disabled form as it is configured in the ADSS Sever under that ADSS Certification Service Profile. Possible certificate purposes could be Document Signing, TLS Server Authentication, Code Signing etc. ADSS Web RA supports the following types of TLS certificates:
When an EV TLS Server authentication certificate is revoked, ADSS Web RA will support only the following six revocation reasons:
In case of external CA this field will be enabled and operator can select certificate purpose. |
Registration Authority Server
The Registration Authority Server section displays the following fields:
|
Field |
Description |
|
RAS Service Address |
Displays the RAS Service Address configured in the certification service profile in ADSS Server. (This field is displayed in a disabled state). |
|
RAS Profile |
Displays the RAS Profile configured in the certification service profile in ADSS Server. (This field is displayed in a disabled state). |
|
Client ID |
Displays the Client ID configured in the certification service profile in ADSS Server. (This field is displayed in a disabled state). |
|
Enable Remote Authorisation |
This checkbox is displayed in a disabled state. It is pre-selected or unselected based on the configuration in ADSS Server. |
|
Enable Virtual ID Registration with Password |
Select this checkbox to require the user to provide a password during the Virtual ID registration process. The password is used for credential authorisation within business applications. |
|
Virtual ID Reset Password OTP Mechanism |
Select the OTP verification method to be used to authenticate the Virtual ID password reset action. The following options are available:
If Both (Email and SMS) is selected, the user must provide two OTPs received via email and SMS to authenticate the password reset action. |
Details
The Details screen consists of the following sections:
- Certificate Period
- Authentications
Certificate Period
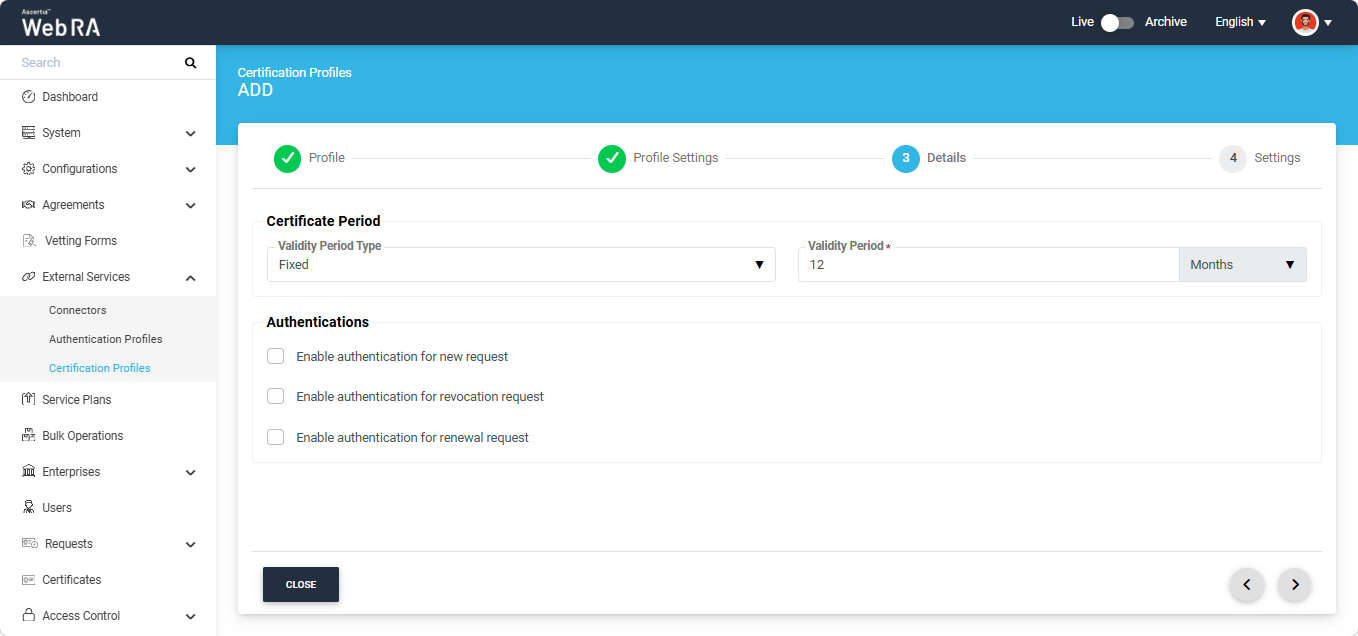
This section consists of the following fields:
|
Field |
Description |
|
Validity Period Type |
The validity period type can be configured as Fixed to prevent the enterprise user from changing the certificate validity period. Alternatively, it can be set to Custom to allow the enterprise user to define the validity period when creating a certificate request. The Fixed and Custom values can only be used in the ADSS Web RA Admin if the selected ADSS Certification Profile has the overridable option enabled for 'Certificate Validity' in the ADSS Server. Otherwise, the validity period type will be shown as Fixed. |
|
Validity Period |
In this field, you can specify a numeric value for the validity period. If the ADSS Certification Profile is configured to use its own time duration instead of taking the validity period from the certificate request, this value will be ignored by the CA server. |
|
Validity Duration |
The time unit of the validity period. It could be minutes, hours, days, months and years. |
Authentications
From the Authentications section, the operator has the option to enable second-factor authentication for new certificate requests, revocation requests, and rekey requests.
If you enable any checkbox, the system displays the ‘Authentication Profiles’ dropdown, from which the operator can select the required profile for second-factor authentication. The available authentication methods include OTP, SAML, Active Directory, Azure Active Directory, and OIDC.
|
|
Note:
|

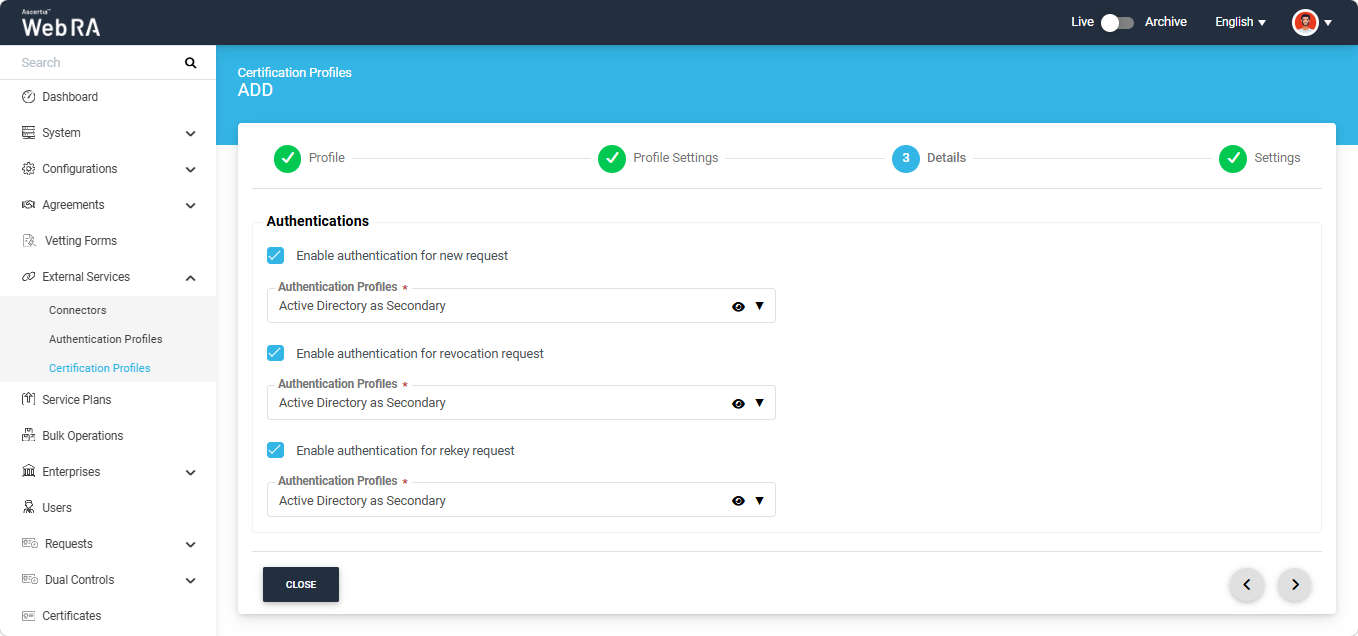
To view the details of an authentication profile, click the ‘Eye’ icon next to the profile name. The system will open the ‘Authentication Profile’ dialog, displaying the Basic Information.
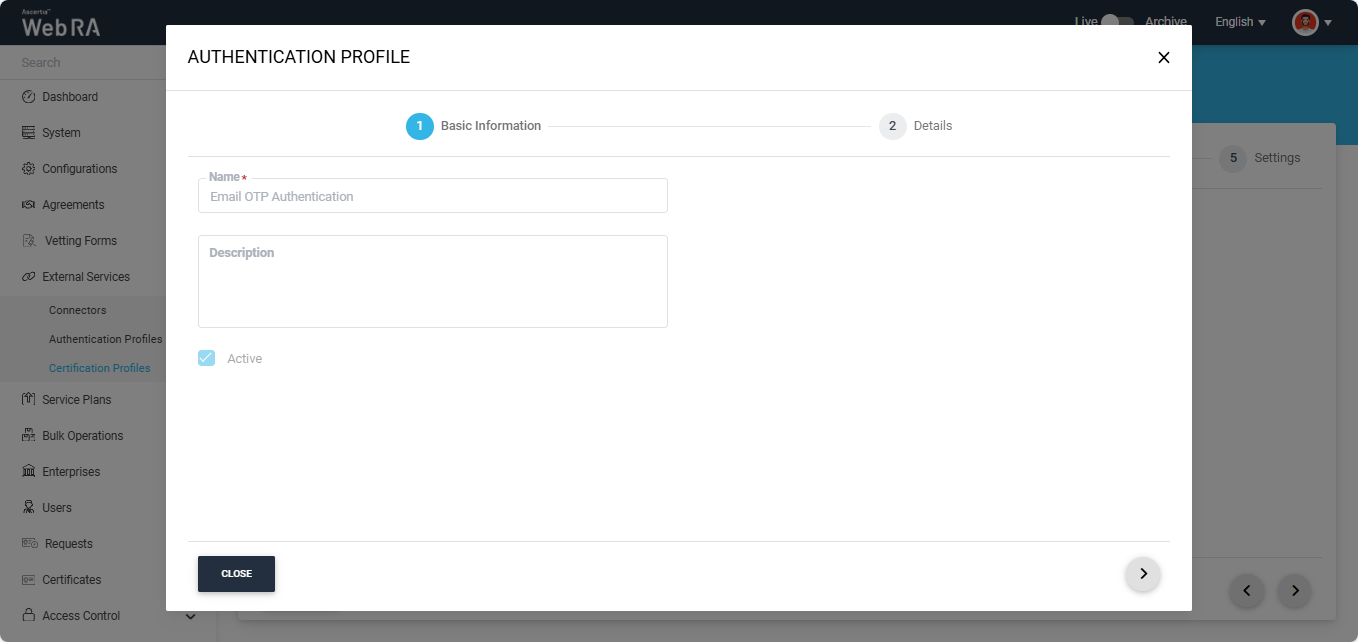
To view the details of the profile, click the ‘Details’ tab.
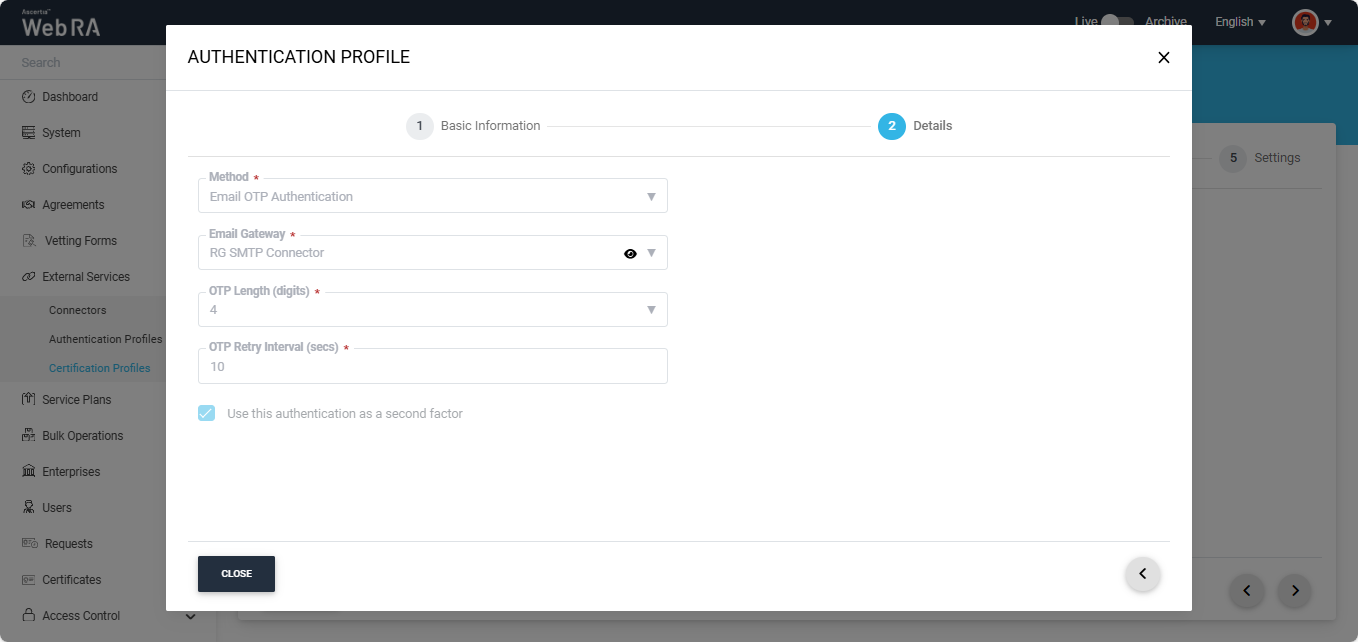
After providing all the required information on the 'Details' screen, click the next ‘>’ button to navigate to the ‘Settings’ screen.
Settings
The 'Settings' screen consists of the following sections:
- Agreement
- Vetting
- Special Permissions
- Digital Onboarding
- Mandatory Fields
Agreement
This section consists of the following fields:
|
Field |
Description |
|
Subscriber Agreement |
From this dropdown the administrator can select a subscriber agreement. A subscriber agreement is selected in a certification profile if the admin wants the user to agree on certain terms before submitting a certificate request. |
Vetting
This section consists of the following fields:
|
Field |
Description |
|
Vetting Option |
This dropdown allows the administrator to choose whether vetting is required for certificate requests generated in the system. By default, the None option is selected. To require vetting for a certificate request, select the Manual Vetting option from the dropdown. |
|
Vetting Form |
This dropdown field appears only when ‘Manual Vetting’ option is selected in the 'Vetting Option' dropdown. It displays a list of all active vetting forms. Select the required form from the list to configure it with the certification profile. |
|
Enable Revocation Vetting |
Select this checkbox to enable vetting for revocation requests. |
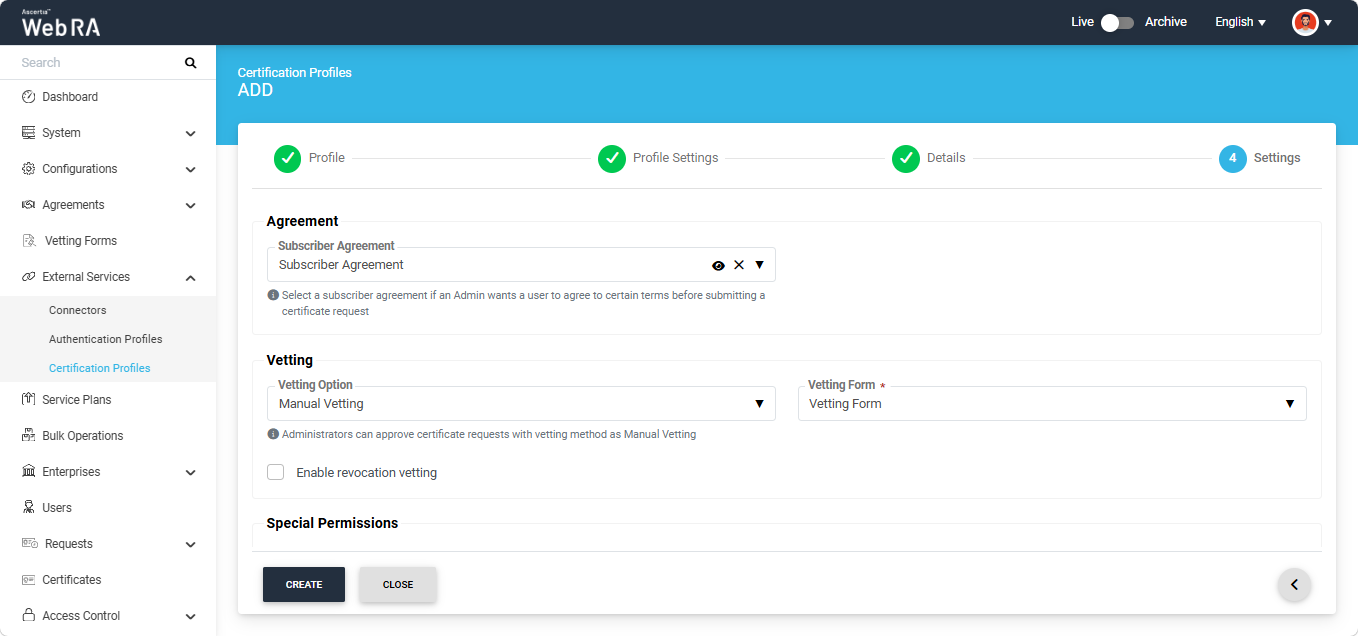
Special Permissions
Special permission configurations allow you to permit creation or revocation of certificates to a specific number of Admin RAO and Enterprise RAO. The certificate creation permissions include creation of new certificates, renewal, rekeying and issuance of certificates.
Note: The 'Special Permissions' section appears only when the 'Manual Vetting' option is selected in the 'Vetting Option' dropdown under the 'Vetting' section.
This section displays the following two fields:
- Vetting Permission
- Enable Certificate Renewal Limit
- Vetting Permission
The Vetting Permission dropdown displays the following options:
- None
- Certificate Vetting Permission
- Revocation Vetting Permission
- Certificate and Revocation Vetting Permission
Note: The 'Revocation Vetting Permission' and Certificate and Revocation Vetting Permission' options will only appear when the 'Enabled Revocation Vetting' checkbox is selected under the 'Vetting' section.
The permissions can be assigned to Admin RAOs, Enterprise RAOs, or both, depending on the approval requirements.
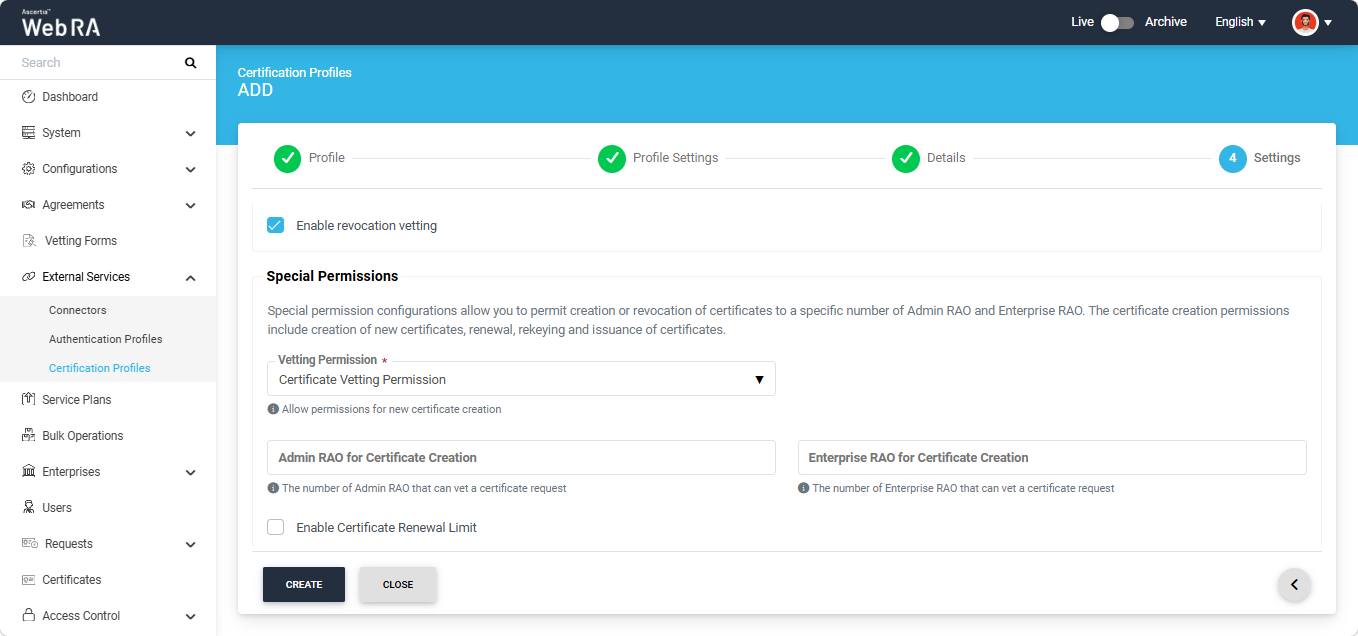
Minimum number of Admin RAO/Enterprise RAO required
The operator must permit at least one Admin RAO or Enterprise RAO for the special permissions. If both fields are set to 0, the following error message will appear on the screen:
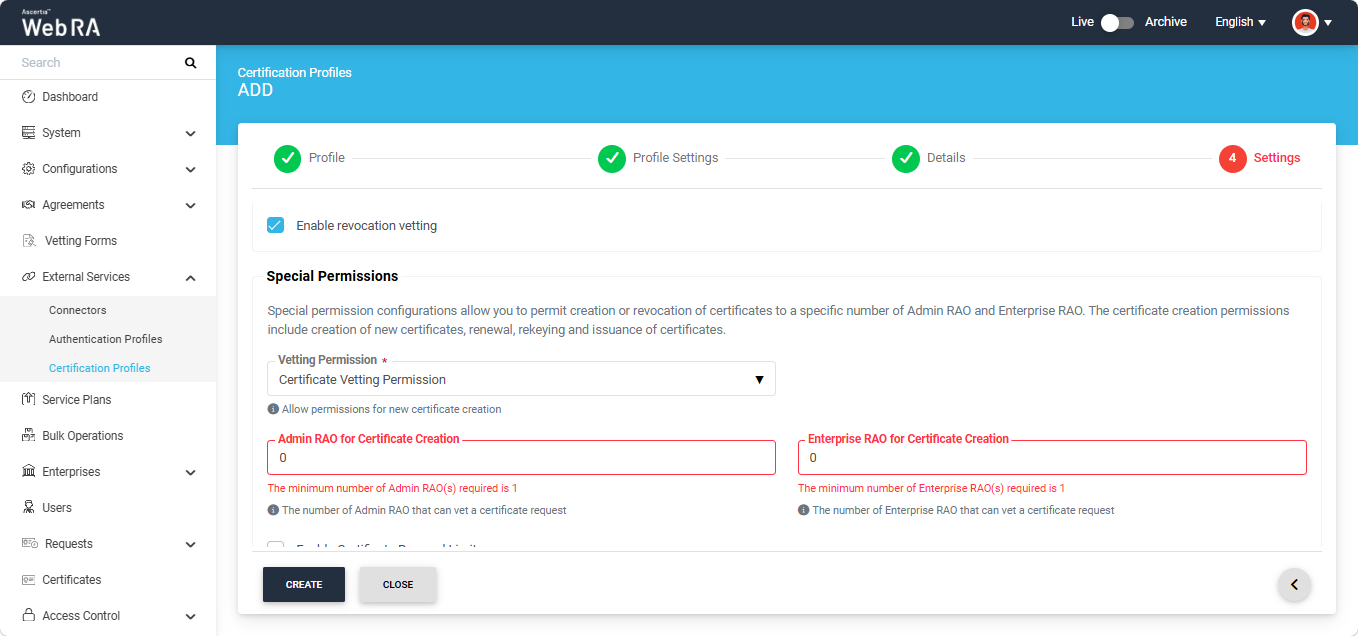
Maximum Limit on the Number of Admin RAOs / Enterprise RAOs
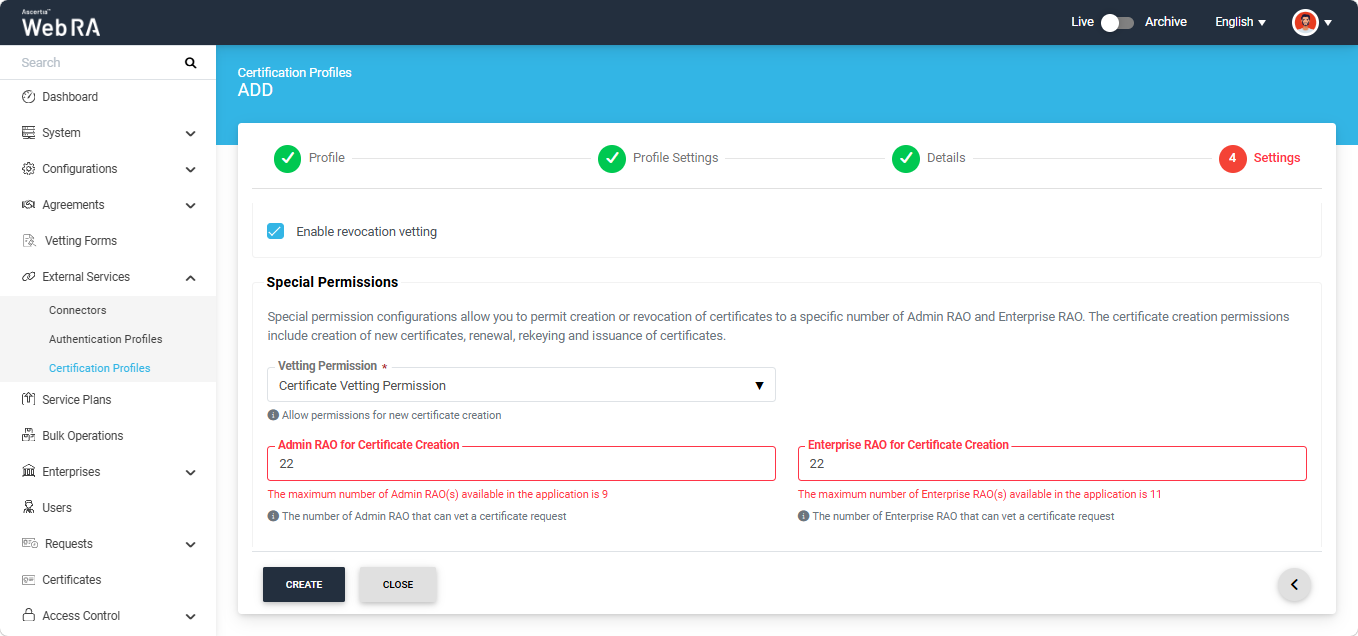
If the operator enters a number greater than the total number of available Admin RAOs or Enterprise RAOs in the Web RA application, the following error message will appear on the screen:
Certificate and Revocation Vetting Permission
Note: This option will only appear in the 'Vetting Permission' dropdown if 'Enable Revocation Vetting' is selected in the 'Vetting' section.
If the operator has selected the ‘Certificate and Revocation Vetting Permission’ option in the 'Vetting Permission' dropdown, the following two additional fields will appear on the screen:
- Admin RAO for Certificate Revocation
- Enterprise RAO for Certificate Revocation
The operator needs to specify the number of RAOs (Admin or Enterprise) that have permission for this action according to the system rules mentioned above.
After making all the required selections, click the ‘Create’ button to finalise the certification profile.
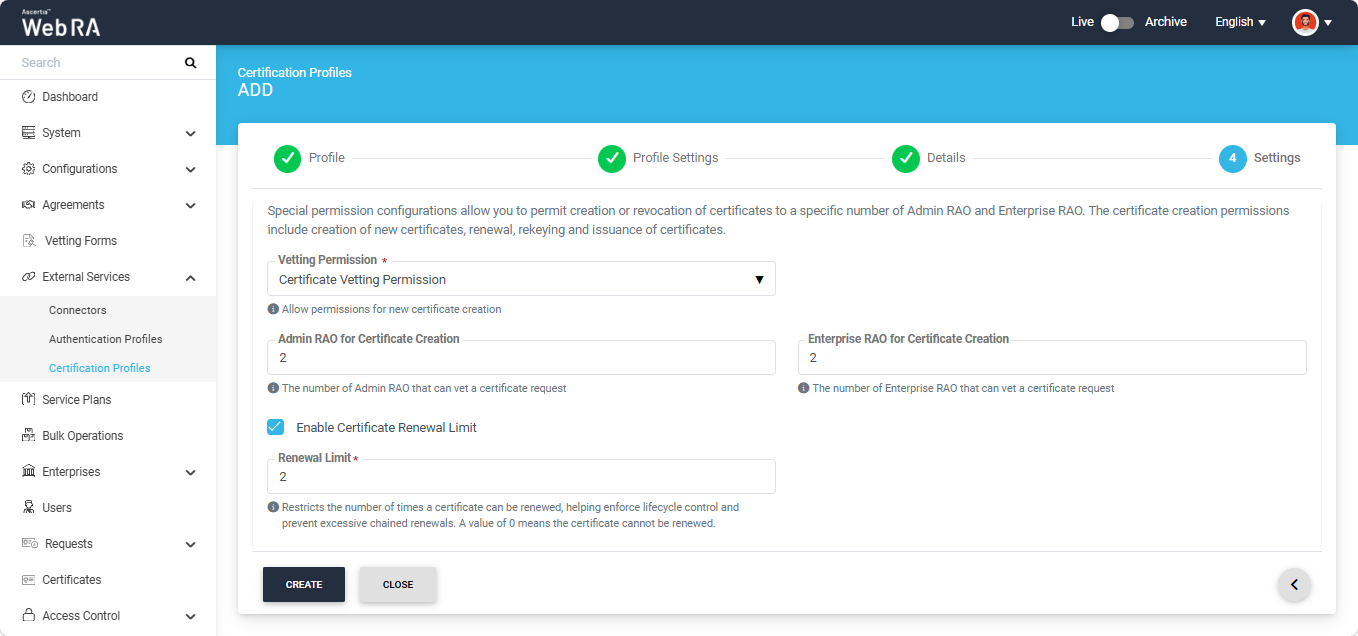
- Enable Certificate Renewal Limit
Note: This checkbox is displayed on this screen only when the 'Renew Certificate' option is selected under 'Certificate Renewal Settings' in the Configurations > Policies > Certificates module.
This section allows the operator to set a limit on the number of times a certificate can be renewed in the Web RA system. The configured limit is applied individually to each certificate generated in the system.
For example, if a Renewal Limit of 1 is configured in the certification profile, a certificate can only be renewed once. Any subsequent attempt to renew the same certificate will result in an error being displayed by the system.
Note: If 0 is entered in the Renewal Limit field, certificates generated under this certification profile cannot be renewed.
Digital Onboarding
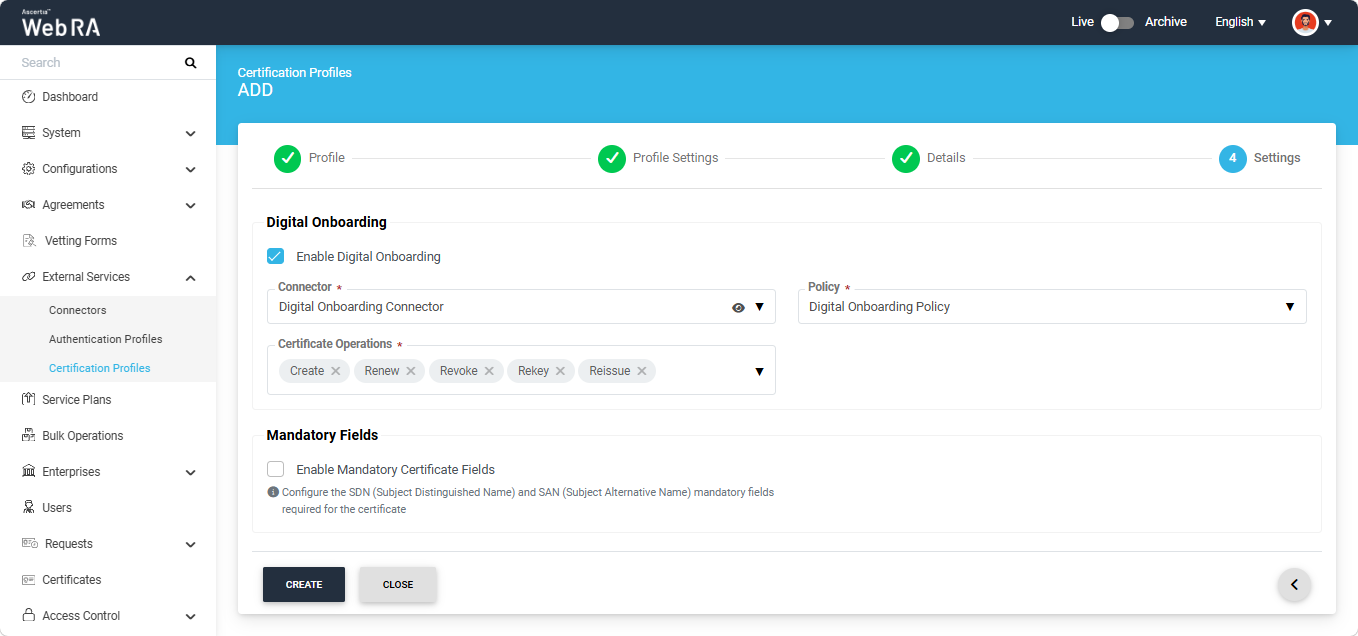
Select the 'Enable Digital Onboarding' checkbox to ensure that users complete the digital onboarding process before performing certificate-related operations in the Web RA system.
When this option is selected, the following fields appear on the screen:
|
Field |
Description |
|
Connector |
Select the connector to be used for the digital onboarding process. |
|
Policy |
Select the digital onboarding policy to be applied during the onboarding process. |
|
Certificate Operations |
Select the certificate operations for which the digital onboarding process is required. Users must complete the digital onboarding process before they can proceed with the selected operation(s). |
Mandatory Fields
This section consists of the following fields:
|
Field |
Description |
|
Enable Mandatory Certificate Fields |
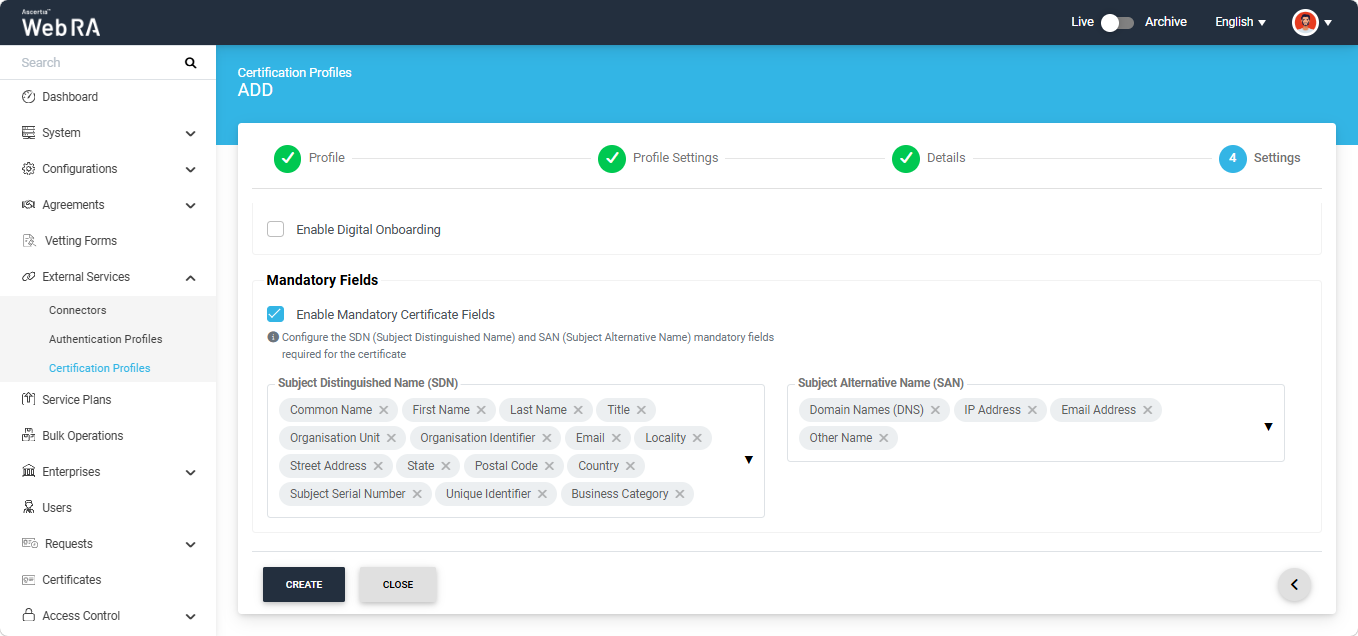
If enabled, this option allows the administrator to define which Subject Distinguished Name (SDN) and Subject Alternative Name (SAN) fields must be mandatory when generating a certificate. Enabling this checkbox will display the SDN and SAN dropdowns, allowing the administrator to select the required mandatory fields while leaving the optional ones unchecked. |
After configuring the required Settings, click the ‘Create’ button to finalize the creation of the certification profile.